LibraryVibecoding News and Updates10 min read
Turn vendor insurance certificates into a review queue
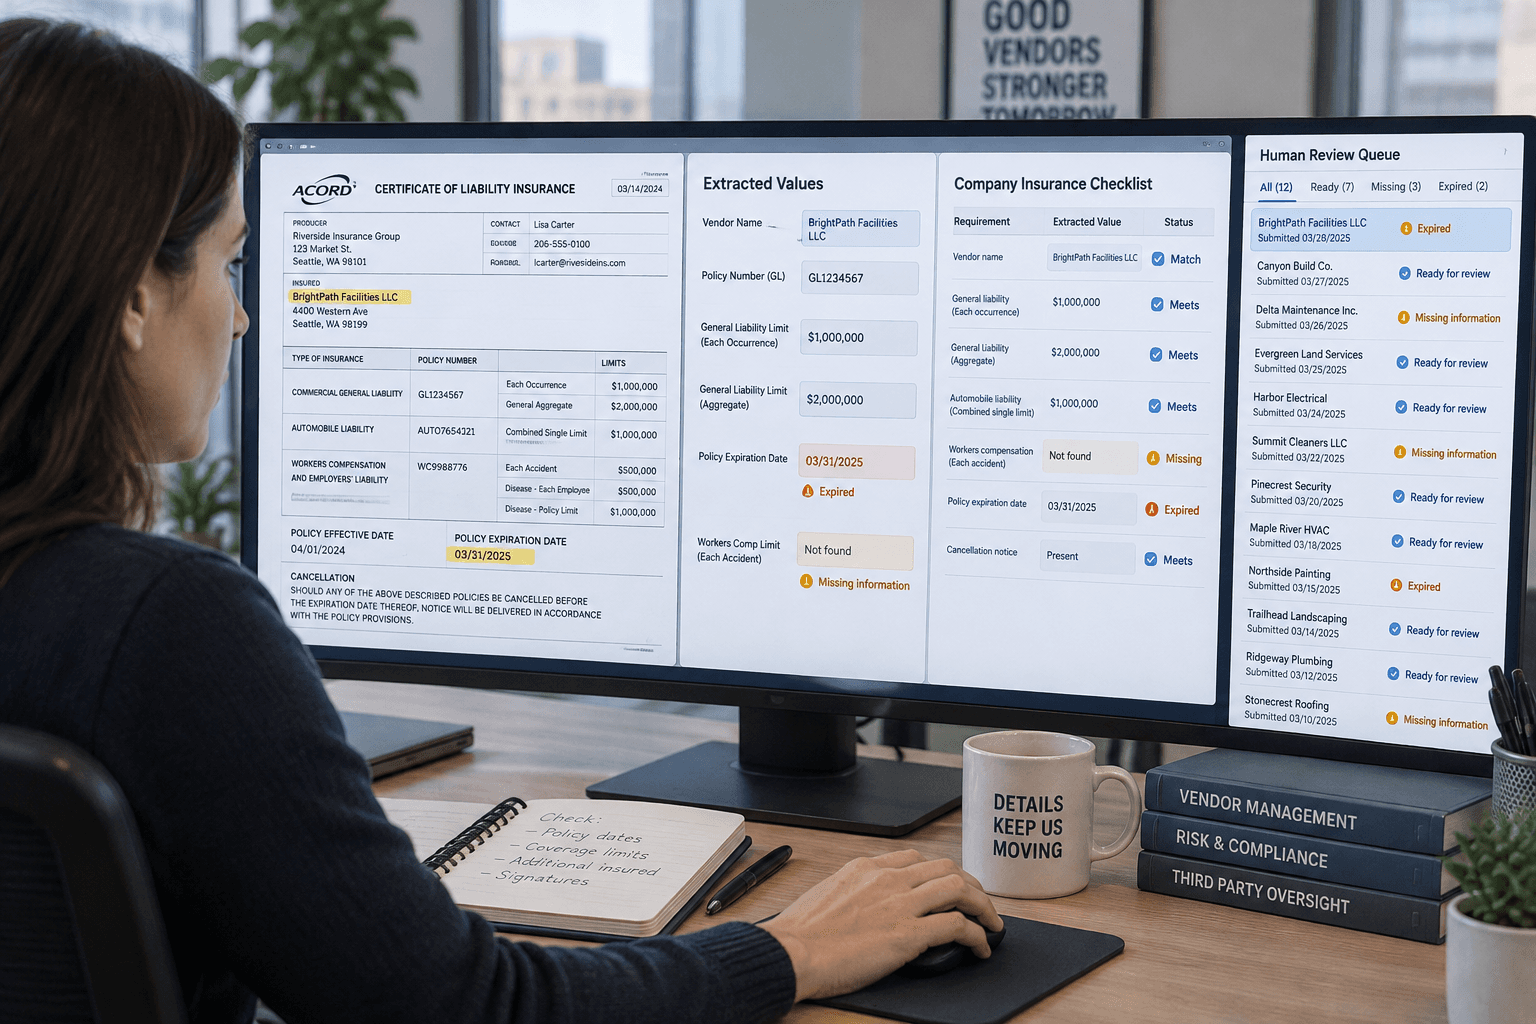
A vendor sends a certificate of insurance. Someone opens the PDF, checks the vendor name and dates, compares a few limits with the contract checklist, then saves it somewhere and updates a spreadsheet. Repeat that for every contractor, event partner, or service provider, and the task becomes a reliable source of small delays and missed follow-ups.
A proposed agent workflow can make that intake easier to review. It reads the certificate, extracts a short list of fields, compares those fields with requirements your organization has already written down, and returns a queue of items for a person to check. It does not decide whether a vendor is insured well enough, approve the vendor, contact the broker, or change the contract record.
That boundary matters. A certificate can be useful evidence to review, but it is not the insurance policy itself. The New York State Department of Financial Services explains that a certificate listing coverage terms does not amend or expand the underlying policy. That state opinion is not a universal legal guide, but it makes the practical point: matching text on a form to a checklist is not the same as determining what coverage applies.
Start with a queue, not an approval bot
The goal is to shorten the clerical path between receiving a document and knowing what needs attention. A reviewer should be able to open a row, see the source document, inspect the extracted value and where it came from, and decide what happens next.
A useful first version needs three inputs:
- The document. A vendor certificate arrives in an approved intake folder or mailbox. The workflow records the original file name and location.
- The vendor record. A stable vendor identifier or name from an existing approved list helps connect the document to the right relationship. A similar company name is not enough to merge records automatically.
- The requirement checklist. The process owner maintains the fields and rules to compare, such as named insured, policy type, stated limits, certificate date, and expiration date. Requirements should come from the contract or the person responsible for risk, not from the agent’s guess about what is customary.
Keep the first run narrow. Choose one document type and a handful of fields that the reviewer already checks. If the business has several certificate formats or contract-specific requirements, don’t make the agent silently generalize across all of them. Add a separate rule set only after the owner has defined and reviewed it.
A proposed flow from PDF to exception list
This is an illustrative workflow, not a build I have run or tested. One possible implementation uses a document extraction service such as Azure Document Intelligence, a small agent or orchestration layer, and a review table in an approved system. Microsoft documents that its layout model can extract text, tables, selection marks, and document structure, and supports PDF and image inputs. That establishes a possible extraction capability, not the accuracy of a certificate-review workflow in your organization.
The workflow could run like this:
- Accept and label the file. The intake step records who or what submitted the certificate, its received date, and its original location. It does not rename the file in a way that loses the original identity or overwrite a previous certificate.
- Extract candidate fields. The document service reads the PDF and returns text and structure. The agent maps likely values into a fixed set of fields: vendor name, named insured, policy type, policy number if required, stated limit, effective date, expiration date, and the page or text snippet supporting each value.
- Validate shape and source. A deterministic check confirms that dates parse, limits are numeric where expected, and every proposed value has a document reference. Missing, contradictory, or ambiguous fields become
needs_review; they do not get filled by inference. An OCR confidence score can help identify fields for review, but it does not tell you whether the insurance is adequate. - Compare with the approved checklist. The workflow compares extracted values to the requirement record for that vendor or job. The comparison should be explicit: “expiration date is earlier than required date” or “stated limit is below the checklist value.” It should not produce a legal conclusion such as “coverage is valid.”
- Write a review row. The output includes the vendor identifier, document link, each extracted value, source location, matching requirement, comparison result, and reason for any flag. A person receives the queue or notification.
- Wait for a person’s decision. The reviewer checks the source document and requirement, then marks the item verified, requests a corrected document, asks the broker or risk owner a question, or records another appropriate next step. The agent does not send those requests or update the vendor’s approval status.
The structured output matters because a paragraph saying “everything looks good” is hard to audit. A row with one field per value and a source link gives the reviewer a direct path back to the evidence. If the extraction service cannot identify a value or the document has multiple plausible values, the right output is an exception with the uncertainty visible.
The checklist is the real policy
The agent cannot supply the organization’s risk requirements. A certificate may display several limits, legal entities, policy dates, endorsements, or notes. Which of those matters depends on the contract, jurisdiction, and review process. Put the approved requirements in a versioned checklist that names the owner and effective date. If a contract changes, update the checklist through the ordinary approval process rather than asking the model to interpret a new clause and treat its answer as policy.
For example, a checklist might say that a specific vendor relationship requires a named insured value to match the vendor’s legal entity and that a particular policy must remain in force through a defined date. The workflow can compare strings and dates, then flag a mismatch. It should preserve the exact values and label its comparison as a clerical check. A human decides whether the difference is meaningful, whether a policy document or endorsement is needed, and whether the vendor may proceed.
This also helps prevent false certainty from a neat table. If the certificate names a parent company while the contract names a subsidiary, a literal mismatch may be important or harmless depending on the documents and legal relationship. The agent has no authority to resolve that. It can show both names, link the source, and ask for review.
Give the agent narrow tools and access
Treat the certificate and any text inside it as material to inspect, not instructions to follow. Documents can contain unexpected text, and an agent should not let document content redirect its task or gain broader access. Limit it to reading the intake folder, looking up the approved checklist, and writing a review row to a restricted destination. It should not have credentials to approve vendors, amend records, send external messages, or delete source files.
Microsoft’s Foundry Agent Service transparency guidance recommends defining allowed and prohibited actions, setting operating boundaries, and providing oversight to review or approve actions. That is useful guidance for this workflow even if you choose another platform. The simplest meaningful boundary is that the agent can create a draft review item but cannot make the business decision or perform the resulting action.
Also decide where the documents and extracted values may be processed and stored. Certificates may include personal contact information or other business-sensitive details. Confirm that the selected service and account are approved for those documents, identify who can see the queue, and set a retention period that fits your records policy. A cloud extraction service sends documents outside your local machine; don’t treat “agent” as a privacy setting.
What can go wrong, and how to recover
A clean-looking output can still be wrong. A scan may be blurry; the document may be rotated; a table may place a limit beside the wrong policy; a date may be read in the wrong format; or a certificate may be expired while a newer file sits elsewhere. Microsoft notes that extraction performance varies by real-world implementation and advises running an evaluation on representative documents. Its Document Intelligence transparency note describes confidence values for extracted words and key-value mappings and calls for a pilot to understand extraction quality. Treat those values as a review aid, not as proof the extracted field is correct.
Build recovery into the result:
- If the file can’t be read, route it to manual intake and preserve the original.
- If a required value is missing, return “not found” with the relevant page or section checked; don’t fill it from another vendor’s document.
- If two documents disagree, show both and ask the reviewer which is current.
- If the agent cannot match the vendor confidently, leave the vendor association unresolved.
- If the requirement checklist is missing, out of date, or internally inconsistent, stop the comparison and contact its owner.
- If a service call fails or times out, make the item visibly incomplete and safe to retry. Avoid creating duplicate rows by using a stable intake-file identifier.
Keep a record of the original document, extraction result, checklist version, agent output, reviewer decision, and any correction. That history lets the team see whether an error came from a poor scan, an incorrect extraction, a stale requirement, or a review mistake. It also makes it possible to correct the process instead of quietly changing a spreadsheet cell with no explanation.
Test whether it helps before widening it
Start with documents your organization is permitted to use, and have a qualified reviewer establish the expected values and outcomes before running the workflow. Include more than polished examples: scanned pages, unusual layouts, multiple policy rows, date formats, missing fields, and documents that should not match a vendor. Do not tune on a file and then count that same file as independent evidence that the workflow works.
For each case, compare the agent’s extracted fields with the reviewer’s answer. Record the number of fields that were correct, missing, or routed for review, and note the kinds of errors. Keep the denominator visible: “four of five expiration dates matched” is more informative than “mostly accurate,” but five examples are still only a small pilot. Make the reviewer confirm every field before a document is accepted during the trial.
Measure the task that matters to the team. How long does it take from receipt to a complete review? How many documents need a person to correct extraction? How many get routed to the wrong vendor or miss a required exception? Include time spent reviewing the output and maintaining the checklist. The workflow has not saved time if it replaces a quick visual scan with a longer audit of opaque model claims.
A sensible first success condition is modest: the queue consistently points a reviewer to the right file, surfaces missing or mismatched fields, and does not make silent changes. If that works across a representative pilot and the organization approves the data path, consider a limited expansion. If the checklist is unclear or the output is difficult to verify, fix those parts before automating more intake.
Keep the decision attached to a person
The useful agent here is a document clerk with a narrow job: read, compare against written requirements, and assemble a review packet. It can remove repetitive copying and make exceptions easier to find. It cannot establish that coverage is legally sufficient, interpret an underlying policy, or decide whether a vendor can start work.
That distinction should appear in the output itself. Label the item “extraction and checklist comparison,” show the evidence, and leave a named reviewer responsible for the decision. If the agent cannot point to the source for a value, the value is not ready to act on.
Before building this, identify the person who owns the insurance requirements and the reviewer who will handle exceptions. If neither role is clear, automate nothing yet. The first task is agreeing on the checklist and the decision path; an agent can only make that process easier to see once the people responsible for it have defined it.
Sources
Every claim above traces back to one of these. Go read them yourself.
- 01Document layout analysis
Microsoft Learn / learn.microsoft.com / retrieved Oct 16, 2026
- 02Transparency note for Document Intelligence
Microsoft Learn / learn.microsoft.com / retrieved Oct 16, 2026
- 03OGC Opinion No. 00-09-04: Acord Form and Certificates of Insurance
New York State Department of Financial Services / dfs.ny.gov / retrieved Oct 16, 2026
- 04Transparency note for Foundry Agent Service
Microsoft Learn / learn.microsoft.com / retrieved Oct 16, 2026
Suggested reading
Selected articles based on topic, tags, and skill focus across the library.
Vibecoding News and Updates
Turn a failed build into an evidence packet
A proposed agent workflow can organize a failed GitHub Actions run into evidence and next checks. It helps a person investigate the failure; it does not diagnose the cause for them.
Vibecoding News and Updates
Use an agent to prepare an access review
A proposed agent workflow can compare an access list with your approved role rules and prepare a review packet. A person still decides who should keep access.
Vibecoding News and Updates
Ask an agent to check one staging user journey
A coding agent can walk through one local preview flow and report what it observed. Keep the test bounded, the data disposable, and the release decision with a person.